View more View less
You're going to need to put in a little more effort to make your case.
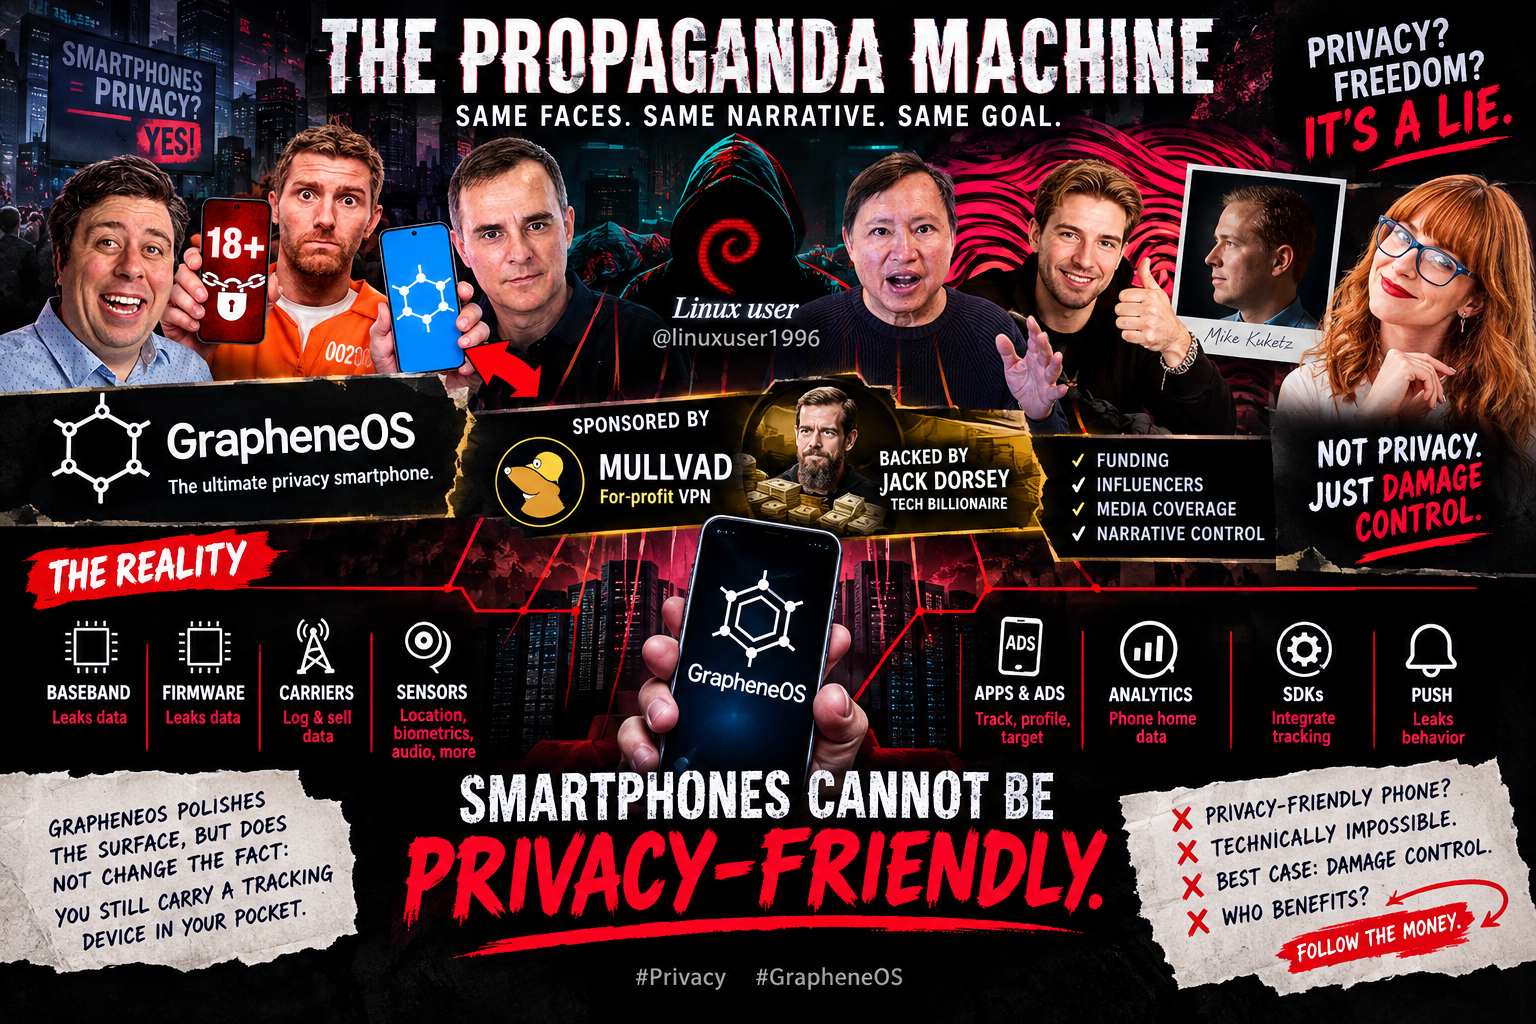
As far as I know, in GrapheneOS everything is carefully isolated to restrict what data goes in or out of the operating system, even communications with the baseband modem. Apps are put into hardened sandboxes and only given access you explicitly grant. This applies even to Google Play Services, which you can also just not install or install in a Private Space or secondary user profile to further limit access. Additionally, GrapheneOS implements the ability to deny applications sensors and network permissions, further limiting information that can be collected or just outright eliminating the ability to send it.
Firmware and microcode remain concerns, but analysis of GrapheneOS network communications hasn't found anything unexpected, leaving this as a "trusting trust" problem. This is also not a concern unique to smart phones, although there's no option to install coreboot and forego microcode updates with smart phones.
Carrier tracking is a legitimate concern, but you don't actually need to install a SIM in a smart phone. Despite the name, they are in fact just small computers.
That's not to say the situation is ideal. Until a genuinely free hardware platform is available, it won't be possible to totally trust any mobile device (and even then we still have to solve trusting trust first) but GrapheneOS seems to be trustworthy enough for the vast majority of users.
It's worth noting that privacy is not the primary aim of GrapheneOS, which is focused on security. Increased privacy is just a precondition of that objective and a nice side effect for its users.
Finally going by that Debian logo, linuxuser1996 is probably running the mainline Linux kernel, with all of its proprietary blobs and likely installing proprietary microcode updates. With horribly out of date software as the cherry on top.
You're going to need to put in a little more effort to make your case.
As far as I know, in GrapheneOS everything is carefully isolated to restrict what data goes in or out of the operating system, even communications with the baseband modem. Apps are put into hardened sandboxes and only given access you explicitly grant. This applies even to Google Play Services, which you can also just not install or install in a Private Space or secondary user profile to further limit access. Additionally, GrapheneOS implements the ability to deny applications sensors and network permissions, further limiting information that can be collected or just outright eliminating the ability to send it.
Firmware and microcode remain concerns, but analysis of GrapheneOS network communications hasn't found anything unexpected, leaving this as a "trusting trust" problem. This is also not a concern unique to smart phones, although there's no option to install coreboot and forego microcode updates with smart phones.
Carrier tracking is a legitimate concern, but you don't actually need to install a SIM in a smart phone. Despite the name, they are in fact just small computers.
That's not to say th
...